Exaforce extends its AI security tool to monitor more than just Claude
While most of these efforts focused on AI agent discovery, a recent study showed that this is only part of the puzzle that enterprises need to solve. A March 2026…
While most of these efforts focused on AI agent discovery, a recent study showed that this is only part of the puzzle that enterprises need to solve. A March 2026…
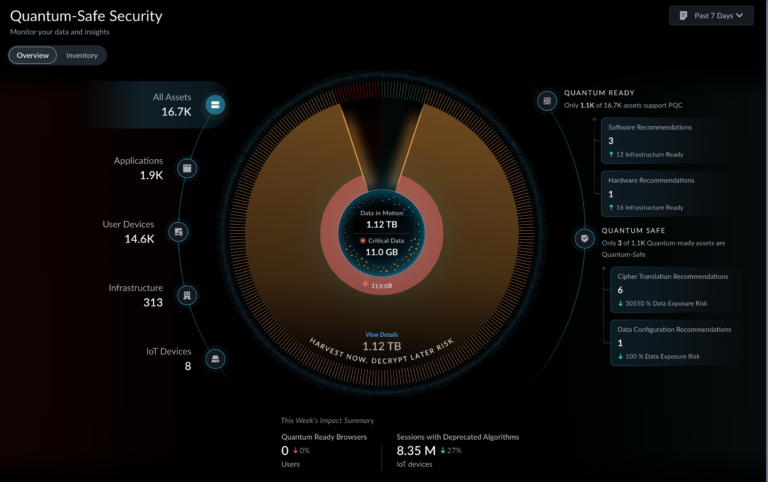
Palo Alto Networks has achieved FedRAMP Moderate authorization for Quantum-Safe Security (QSS), a turnkey Automated Cryptography Discovery and Inventory (ACDI) solution. With this certification, federal agencies can deploy QSS immediately. …
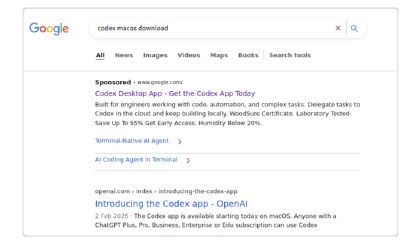
Executive Summary Attackers are using a fake Codex download experience to trick macOS users into pasting a malicious command into Terminal. This technique, known as ClickFix, relies on social engineering…
Software supply chain attacks pose a critical enterprise threat. In the first half of 2026, these attacks increasingly used malicious software packages uploaded to public software registries, the CrowdStrike 2026 Threat…
Open-source registries for AI agents are only effective when they include a rigorous, transparent security review process for community submissions. That’s why for its new CyberAgents Exchange registry, Tenable paired…
Over the last month, Okta has observed an increase in the frequency and scale of credential stuffing attacks targeting online services, facilitated by the broad availability of residential proxy services,…
What a short, intense rotation taught me about uncertainty, evidence, and working alongside AI in the SOC. Let me get one thing out of the way: I am not a…
In this article Threat actors are increasingly improving their tactics to make suspicious emails look like legitimate email notifications to potential victims, deploying techniques that impersonate internally sent emails from…
Executive Summary In this research we introduce a prompt-crafting technique for bypassing quick LLM-based policy checks — using plain English (no emojis, base64, invisible formatting, etc.) A policy-violating payload (e.g. ”encrypt…
Today, we’re making Cloudflare CASB more powerful than ever by introducing automatic remediation policies. This means security teams can now design event-driven logic to revoke risky file shares and dispatch…